
An evaluator asks how a control works in practice, and your team has to piece together the answer from client files, spreadsheets and staff systems. The challenge isn’t simply finding a policy. It’s showing that the documented process is followed, evidenced and acted on. If you’re working out how to demonstrate AML compliance to auditors, connect each control to proof of operation and any resulting follow-up.
That can feel like a substantial task, particularly if preparation has been left until the last minute. A clear evidence trail makes it more manageable and helps reveal whether records reflect what happens in client work and firm-level oversight. For Australian firms subject to AML/CTF obligations, an independent evaluation considers both program design and operational effectiveness, so written procedures need to align with practice.
This guide explains how to organise evidence, assign ownership for audit requests and track actions through to completion. You’ll learn how to map controls to records such as due diligence, risk assessments, monitoring, reporting and staff training, then present them clearly so you can respond to questions without avoidable disruption.
Key Takeaways
- Define the scope of the auditor’s engagement before gathering records, so your evidence pack is relevant rather than a document dump.
- Map each applicable AML/CTF control to its owner, evidence source, period covered and any follow-up required.
- Use a request log to coordinate how to demonstrate AML compliance to auditors, track responses and make ownership clear.
- Assess whether an issue is a missing record or a weakness in how a control operates before deciding on next steps.
- Choose repeatable workflows that support traceable, accessible records and help keep evidence organised between evaluations.
Demonstrating AML Compliance: Start With the Scope
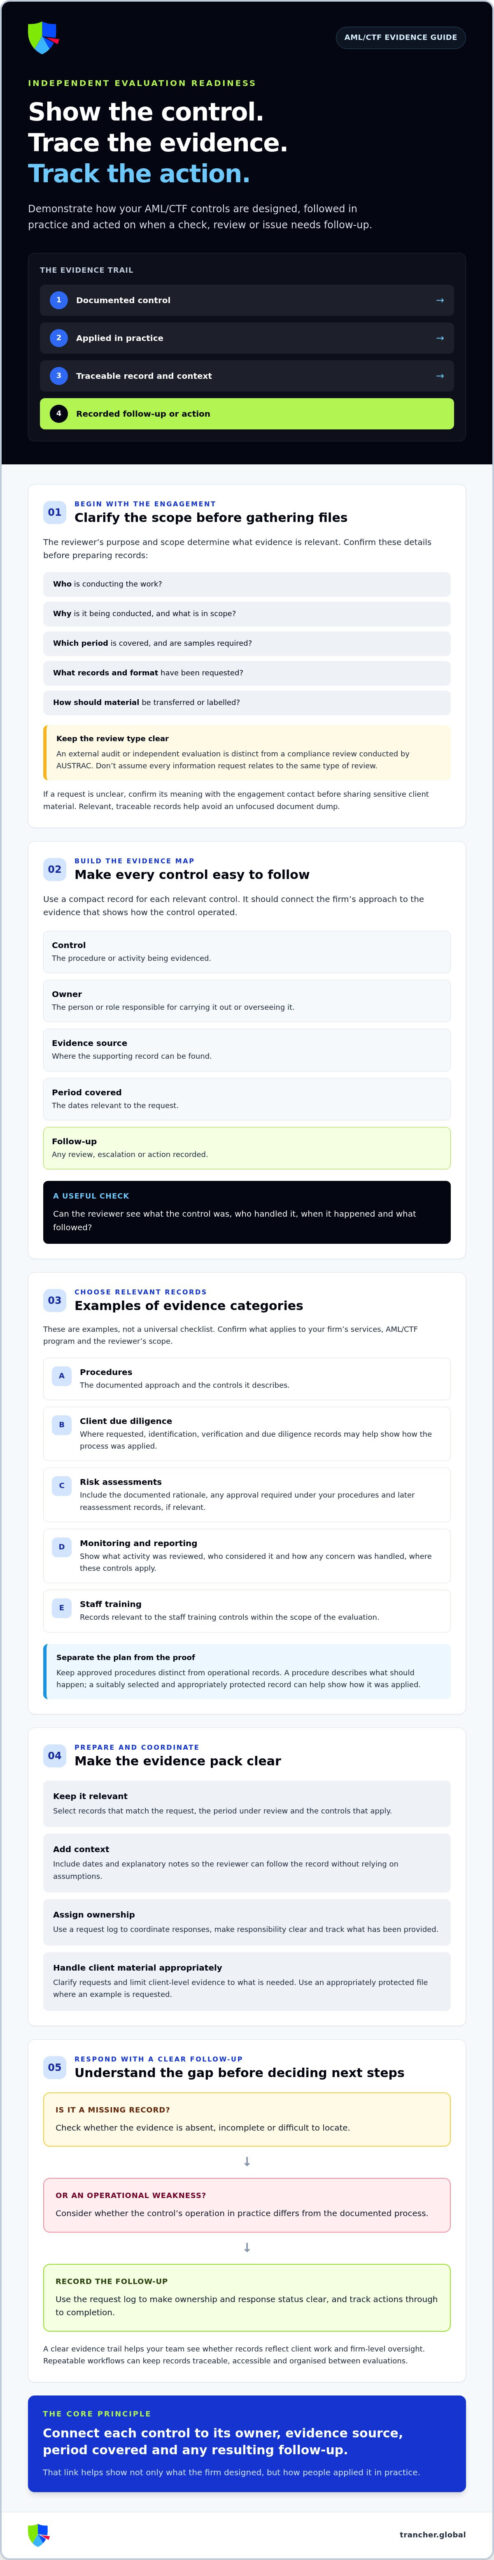
To demonstrate AML/CTF compliance, show which controls apply to your firm, how they operate in practice and what happens when a check, review or issue requires follow-up. A written program explains the intended approach, but it doesn’t prove that staff apply it consistently. The evidence needs to connect the procedure to what happened, when it happened and how the firm responded.
Start with the engagement, not a mass export of files. The reviewer’s purpose and scope determine what they’ll ask to see, and the records required will depend on your firm’s services and AML/CTF program. Evidence should be relevant, traceable to a source, current for the period under review and presented with enough context to be understood.
Clarify the audit or review before gathering records
Confirm who is conducting the work, why it is being conducted, the period covered, its scope, the records requested and the preferred submission format. An external audit or independent evaluation is distinct from a compliance review conducted by AUSTRAC. The Australian Transaction Reports and Analysis Centre (AUSTRAC) is Australia’s AML/CTF regulator, but don’t assume every information request relates to the same type of review.
If a request is unclear, ask the engagement contact what it means before sharing sensitive client material. Clarify the date range, whether samples are required and how records should be transferred or labelled. This keeps the response focused and reduces unnecessary handling of confidential information.
Build an evidence map around the firm’s AML/CTF program
List each relevant control alongside the accountable role, supporting record and date it was last reviewed. Depending on the engagement, evidence categories might include procedures, client due diligence records, risk assessments, monitoring activity, reporting records or staff training. Treat these as examples, not a universal checklist. Confirm which controls and records apply to your firm and the reviewer’s scope.
Where requested, connect firm-level procedures with client-level examples. A procedure may describe how a risk assessment is completed; a suitably selected and appropriately protected file can help show how that process was applied. Include dates and explanatory notes so the reviewer can follow the record without relying on assumptions.
Evidence should show both the control the firm designed and the way people applied it, with a traceable record of any resulting action. That link is the foundation of how to demonstrate AML compliance to auditors. It also gives your team a practical starting point for organising requests and identifying gaps before submission.
Map AML/CTF controls to evidence that shows they operate
Once the scope is clear, use a compact matrix to show how each relevant control works in practice. This gives the reviewer a route from the firm’s documented approach to the records that support it, without treating every possible record as a universal requirement.
For each control, record:
- Control: the procedure or activity being evidenced.
- Owner: the person or role responsible for carrying it out or overseeing it.
- Evidence source: where the supporting record can be found.
- Period covered: the dates relevant to the request.
- Follow-up: any review, escalation or action recorded.
Keep approved procedures separate from operational records. A policy can describe how a client risk assessment should be completed; the assessment record, its rationale and any approval can help show whether the process was followed. Check each example against your firm’s services, program and the reviewer’s request before including it.
Show client due diligence and risk decisions consistently
Where the scope calls for client-level evidence, relevant identification, verification and due diligence records may help demonstrate how the firm applied its process. Show the decision trail, not just the final classification. Include the documented risk rationale, any approval required under your procedures and later reassessment records, if relevant. Limit the material to what’s requested and handle client information appropriately. The published guide CDD and KYC Requirements Australia: The 2026 Accountant’s Guide offers further context on these topics.
Evidence monitoring, reporting and staff oversight
For applicable monitoring controls, assemble records that show what activity was reviewed, who considered it and how any concern was handled. Escalation notes and decision trails can make the sequence clear. Redact or exclude unrelated client details where appropriate. If reporting records are in scope, include relevant supporting rationale and check current AUSTRAC guidance before describing or presenting reporting processes.
Staff training records, role ownership and governance reviews may also help demonstrate how responsibilities are communicated and overseen, where they apply to the request. A useful evidence trail lets a reviewer follow the control from procedure to action and any recorded follow-up.
Traceable records connect a documented control to the work performed, the decision made and any resulting action. This is central to how to demonstrate AML compliance to auditors without relying on policies alone. Structured workflows can help keep controls, owners and supporting records connected. Explore AML/CTF workflow and record-keeping support as one option for organising that evidence.
Prepare an auditor-ready evidence pack without a document dump
A focused evidence pack helps a reviewer locate relevant records and understand what they demonstrate. It also helps your team manage requests without pulling sensitive information into an untracked pile of files. Use a consistent process and maintain a master request log showing each item’s owner, due date, source, status and response.
Work through the preparation in sequence:
- Assign a coordinator to manage requests and keep communication consistent.
- Index each request in the master log, clarifying what is needed and the period it covers.
- Gather records from the identified source, keeping the relevant control or request in view.
- Check each item for accuracy, completeness and appropriate handling before sharing.
- Submit the evidence in the agreed format and through an approved secure channel.
- Track what happens next, including submission dates, clarification requests and responses.
Limit access to people who need to prepare, review or submit the material. Use your firm’s approved storage and transfer methods for client and AML/CTF information, and avoid sending records through unapproved channels. For more on organising documentation, see Audit-Ready Compliance Records: The 2026 Guide for Australian Accounting Firms.
Check every record before it goes to the auditor
Check that each record covers the requested period, is complete and legible, and is the correct version. Compare it with the relevant procedure so any differences are visible rather than obscured. If evidence isn’t available, record that plainly in the request log, including the reason, responsible owner and planned next action. Remove unrelated sensitive material only where appropriate and consistent with your firm’s requirements.
Present evidence with a clear index and explanation
Group records by request or control, then use consistent file names and cross-references so the reviewer can follow them. A brief cover note can state what each item demonstrates and the period it relates to. Keep a copy of the submitted pack, and log any clarification requests and responses so the team has a clear record of what was provided.
A well-organised pack supports how to demonstrate AML compliance to auditors: relevant evidence is easy to find, its context is clear and each response has an owner. Structured workflows and record keeping can reduce manual gathering. Explore AML/CTF documentation workflows as one way to keep evidence and activity organised.
Respond to gaps and auditor questions with a defensible follow-up process
A question or missing record isn’t, by itself, proof that a control failed. First establish what the reviewer is asking, what evidence exists and whether the issue relates to record keeping or to how the control operated. A measured response is more useful than a defensive one: set out the facts, explain any limitations and document what the firm will do next.
For each question or observation, maintain a record of:
- The question or finding and the control it relates to.
- Evidence provided, including any limitation or uncertainty.
- Response owner and current status.
- Agreed next step, with an accountable owner and review date.
This creates a clear trail from the reviewer’s concern to the firm’s response and any resulting action. For further perspective on assessing your program, see AML Compliance Health Check: Is Your Program Defensible?
Handle missing, inconsistent or late evidence transparently
Identify the affected control and distinguish what the available records show from what remains uncertain. For example, a missing approval record may be a documentation gap, while evidence that a required decision was not made may point to a control weakness. Establish the cause before drawing conclusions. Record any immediate containment or corrective action, then assign an owner and review date for the next step.
Keep explanations factual and proportionate. Don’t claim a process was followed if the records can’t support that conclusion. If evidence is incomplete, say what is available, what is missing and how the firm is checking the position. This gives the reviewer a more reliable account and helps the firm decide whether further investigation or remediation is appropriate.
Turn observations into tracked improvements
Use an action register to manage issues through to closure. For each item, capture the finding, the firm’s risk rationale, an accountable owner, a milestone and the evidence needed to confirm completion. Record management decisions and approvals where relevant to your governance process. Close actions only when the supporting evidence is available, not simply because a task has been marked complete.
Look for patterns across findings. Repeated errors may point to a workflow that needs clarification, staff who need further guidance or records that are difficult to maintain consistently. Use those observations to strengthen the process, then retain evidence of the change and any later review. This turns audit follow-up into a practical improvement cycle rather than a list of unresolved comments.
A structured AML/CTF workflow can help connect questions, owners and follow-up records. Explore AML/CTF program workflows and record keeping to see how Trancher may support a more traceable process.
Use repeatable AML systems to stay ready between audits
Audit readiness is easier to maintain when AML/CTF work has clear owners and consistent workflows throughout the year. A last-minute evidence sprint can gather documents, but it may not show whether records are kept consistently or follow-up is completed. Build readiness into regular client and firm-level processes instead.
Manual records can work, but files spread across folders, spreadsheets and staff systems may make ownership and retrieval harder to follow. A structured compliance workflow can help connect relevant clients, controls, decisions and actions in one process. Neither approach removes the need for firm oversight. People remain responsible for applying procedures, exercising judgement and checking that records accurately reflect what happened.
When assessing a system or workflow, consider whether it supports:
- Traceability: Can you follow a record back to the relevant client, control, decision and follow-up?
- Access controls: Can access to sensitive information be managed in a way that fits your firm’s requirements?
- Reporting: Can you review compliance activity and identify outstanding actions?
- Workflow fit: Does it support the way your firm carries out relevant AML/CTF processes?
- Exportable records: Can you retrieve records in a useful format for an authorised review?
Assess the practical details before relying on any system. Check who can update records, how changes are tracked and whether information can be reviewed in context. Software can help organise evidence and reduce manual gathering, but it can’t replace effective governance, staff understanding or sound decisions.
Choose practical next steps for the firm
Start with one evidence gap. Assign an owner, agree a review date and check that the updated record shows what changed. This small, accountable action is more useful than adopting a new tool without a clear process for using it. For more context on AUSTRAC reviews, see What Happens During an AUSTRAC Audit? A SME Guide.
Trancher supports Australian accounting firms with structured AML/CTF workflows and audit-ready record keeping, helping organise compliance activity and its supporting evidence. It’s one option to consider if your current process makes ownership, retrieval or follow-up difficult. A platform supports the firm’s process; it doesn’t guarantee compliance on its own. To discuss whether structured workflows may suit your firm, start a conversation with Trancher.
With consistent processes and clear ownership, how to demonstrate AML compliance to auditors becomes an ongoing operational practice, not a task saved for the next review.
Make audit readiness part of your AML/CTF process
A strong audit response connects each relevant control to evidence of how it operates and any follow-up action. Start by confirming the review scope, then organise records so their source, period and context are clear. If a gap emerges, assess it carefully, document the facts and track agreed improvements through to completion.
That’s the practical answer to how to demonstrate AML compliance to auditors: maintain clear ownership and reliable records as part of everyday work, rather than relying on a last-minute search. The right workflows can support consistency, while your people remain responsible for applying procedures and making sound decisions.
Trancher supports Australian accounting firms with structured workflows for client due diligence, risk assessment, monitoring and reporting, alongside audit-ready documentation and record keeping. Dedicated onboarding and local Australian support are also available. Start a conversation about a structured, audit-ready AML workflow and take a practical next step towards stronger ongoing readiness.
With clear processes and steady follow-through, audit preparation can become more manageable and your compliance evidence easier to trust.
Frequently Asked Questions
What evidence should an accounting firm provide to demonstrate AML compliance?
Provide evidence that matches the reviewer’s scope and shows relevant controls in operation. Depending on the request and your firm’s services, this may include client identification and due diligence records, risk assessments and rationales, monitoring activity, reporting records, staff training evidence and governance reviews. Include the relevant period and context for each item. These are examples, not a universal checklist, so confirm what applies before sharing records.
Is an AML/CTF program document enough to satisfy an auditor?
No. A documented program explains the firm’s intended controls, but it doesn’t, by itself, show whether staff follow them consistently. Support relevant procedures with operational records, such as completed client risk assessments, monitoring notes or evidence of staff training, where these are within scope. The reviewer’s requirements will vary, so confirm what evidence is needed to show both the program’s design and how it operates in practice.
How do you prepare for an AML compliance audit?
Start by confirming who is conducting the review, its purpose, scope, period and evidence format. Assign a coordinator, log each request with an owner and due date, then gather and check the relevant records. Provide an index or short explanation for each item, use an appropriate secure method to submit sensitive information, and retain a copy of what you provide. Track questions and follow-up actions through to resolution.
Can software help demonstrate AML compliance to auditors?
Yes. A structured system can help organise records, link activity to clients and controls, clarify ownership and track follow-up. When assessing software, consider traceability, access controls, reporting, fit with your workflows and whether records can be exported in a useful format. Technology supports the process, but it doesn’t replace staff judgement, oversight or accurate record keeping. Your firm remains responsible for ensuring that records reflect what actually happened.
What should a firm do if it cannot find evidence an auditor requested?
Don’t guess or imply that a control was completed if you can’t support that claim. Identify the control, record what evidence is available and explain what remains uncertain. Log the reason the requested record is missing, who will investigate and the next action. Assess whether this is a documentation gap or a control weakness, then assign an owner and review date for any agreed corrective action.
Is an AUSTRAC compliance review the same as an external audit?
No. An AUSTRAC compliance review is conducted by the regulator, while an external audit or independent evaluation is conducted by an evaluator engaged for that purpose. They are distinct processes, and their scope and requests may differ. Confirm who is conducting the review and why before preparing records. For an AML/CTF program independent evaluation, current Australian requirements include a minimum frequency of once every three years, with frequency appropriate to the business.
How often should AML compliance evidence be reviewed?
Keep evidence current as relevant work occurs, rather than waiting until an audit request arrives. Regular checks can help identify missing records, inconsistent decisions or follow-up actions that haven’t been completed. Set review points that suit your firm’s processes and the scope of its AML/CTF program. Separately, current requirements call for an independent evaluation at least every three years, with frequency appropriate to the firm’s size, nature and complexity.